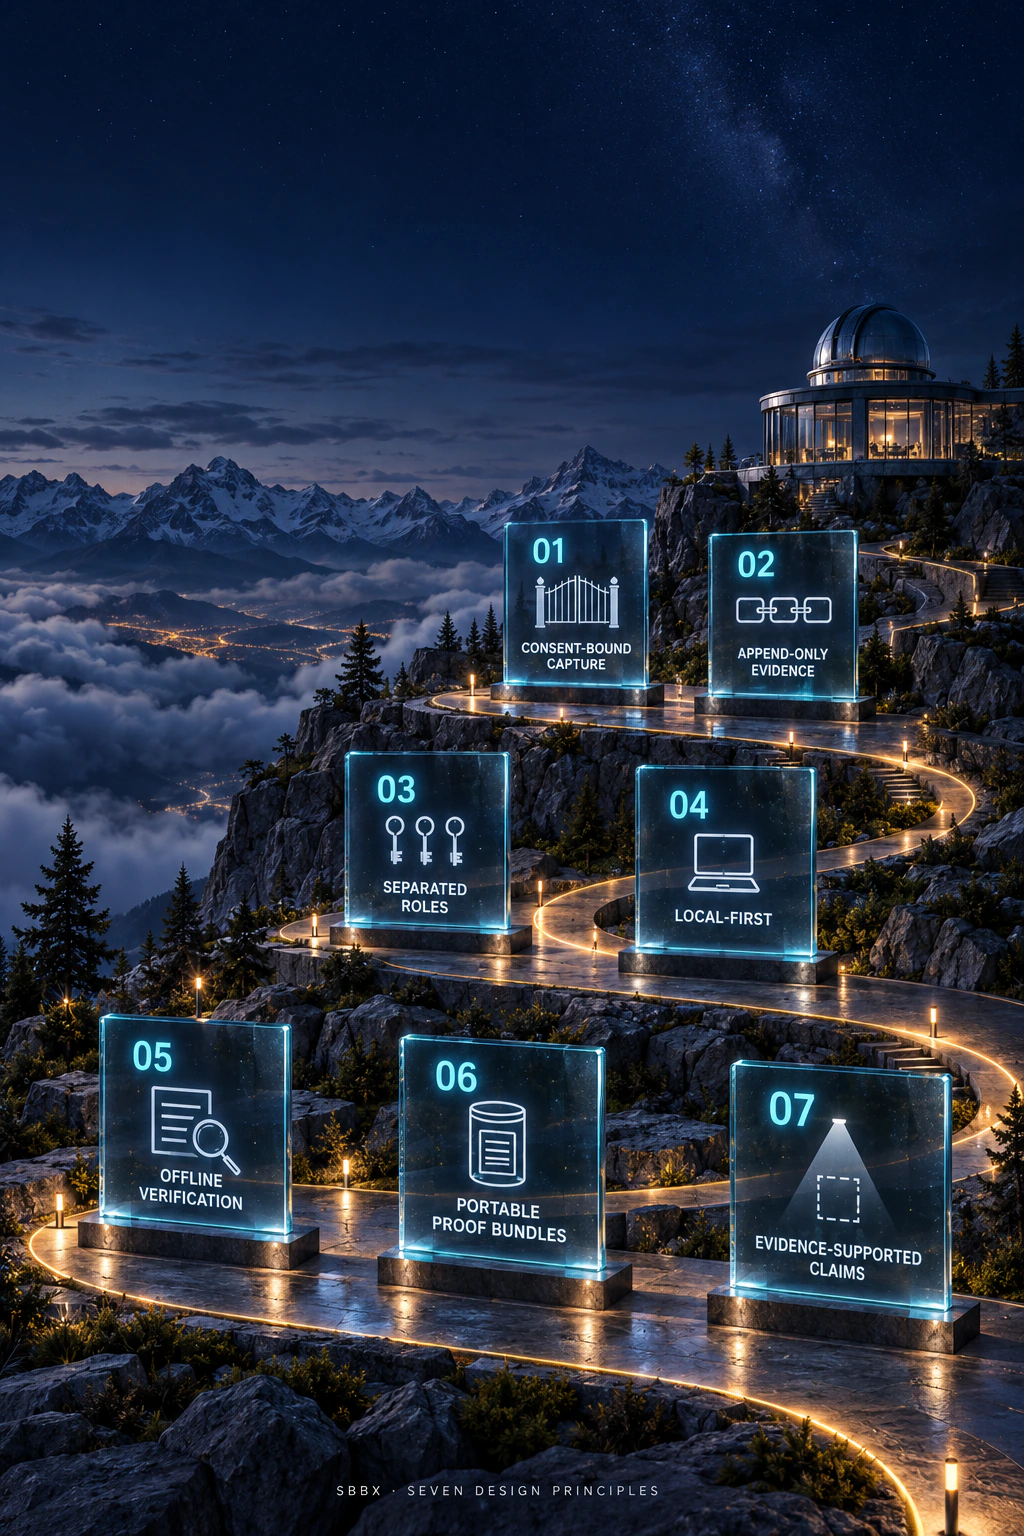
An evidence protocol designed so that verification does not require trusting the producer.
SBBX is open-core and local-first. It is under active development, and each capability below is bound to a declared project state rather than a release claim.
Design properties
Seven properties define the protocol boundary.
These seven properties explain the SBBX design. Implementation, verification and release status are assessed separately; an illustration is not evidence that a capability is complete.
Concept illustration 01 — Consent-bound capture
Capture is intended to stay within an explicitly authorised scope.
Purpose
SBBX is designed to record selected AI-work evidence within a boundary the operator understands and authorises. That boundary should identify the source, the permitted information and the purpose of capture. Recording a work session should not silently become permission to monitor unrelated activity.
How it is intended to work
A capture path should operate within an explicit consent scope. Evidence should distinguish what the system directly observed from what a person or importer supplied. When consent ends or changes, future capture must respect the new boundary.
Example
An operator authorises capture of one development session. That authorisation does not automatically extend to other conversations, repositories or applications.
Boundary
Recording consent is not proof that every relevant event was captured. Revoking future capture does not, by itself, erase previously recorded evidence or establish a retention policy.
Concept illustration
Concept illustration 02 — Append-only tamper-evident evidence
Preserve recorded history and make inconsistencies detectable within the verification boundary.
Purpose
SBBX is designed around an ordered evidence history. Corrections should be represented by additional records that explain the change, preserving the earlier record and its context.
How it is intended to work
Records are linked through cryptographic digests. A verifier can recompute the specified relationships and compare them with the supplied references. The result must identify what was checked and which inputs or trusted references were available.
Example
A later correction can explain that an earlier entry was inaccurate while retaining both entries and their relationship.
Boundary
Tamper-evident does not mean impossible to modify. Verification of supplied records does not, by itself, establish that omitted events never existed, that the entire history was supplied or that the recorded statements are true.
Concept illustration
Concept illustration 03 — Separated capture, approval and consent roles
Recording an action, approving it and consenting to capture are distinct responsibilities.
Purpose
SBBX separates the authority to capture evidence from the authority to approve an action and from the authority to grant consent. A recorded agent output must not acquire human approval simply because it entered the evidence history.
How it is intended to work
The architecture assigns distinct roles to capture, human approval and consent. Their evidence should remain attributable to the relevant role and scope. A connector that records activity should not automatically gain approval authority.
Example
An agent proposes a code change. The capture path records the proposal. A separate human decision records whether that particular change was approved.
Boundary
A role label alone does not prove identity, key protection or valid authorisation. Those claims require their own verification and supporting evidence. This explanation does not claim completed device-level approval proof.
Concept illustration
Concept illustration 04 — Local-first operation
Keep core evidence work under the operator’s control, with clearly scoped remote dependencies.
Purpose
SBBX is designed so that core evidence work can take place on operator-controlled hardware. Local operation supports use without a mandatory central service for every action and makes the storage and capture boundary easier to understand.
How it is intended to work
The architecture places local capture and storage at the centre. External connectors, transfers and optional services have separate purposes and boundaries. Their presence must not be confused with a requirement to upload every record.
Example
An operator works with locally held evidence and later chooses a defined export for another reviewer.
Boundary
Local-first does not mean every feature or this website uses no network. Local storage also does not guarantee survival after uninstall, device loss or key loss. Durability, export, restore and retention require separate evidence.
Concept illustration
Concept illustration 05 — Offline independent verification
Evaluate supplied evidence without asking the producing service to declare it valid.
Purpose
SBBX is designed to let an independent reviewer inspect evidence using a verifier and the required verification material. The producer’s interface should not be the sole authority for the result.
How it is intended to work
A verifier evaluates the supported format and applicable integrity, signature and structural rules using the supplied inputs. Its report should state the evaluated scope, unsupported cases and missing prerequisites.
Example
A reviewer receives an exported evidence bundle and evaluates its supported checks on another computer without contacting the system that produced it.
Boundary
Offline verification does not prove the truth of recorded content, complete capture or current external trust information. A browser demonstration that compares SHA-256 digests is not a substitute for a complete bundle-verification result.
Concept illustration
Concept illustration 06 — Portable proof bundles
Package scoped evidence so another reviewer can inspect it independently.
Purpose
A proof bundle is intended to carry a defined set of evidence beyond the original application. Its structure should make the included records, verification material and declared scope understandable to another reviewer.
How it is intended to work
The export should identify its format and contents and provide the material required for the checks it claims to support. Missing material and unsupported checks must remain visible rather than being presented as successful verification.
Example
A software team shares evidence for a selected AI-assisted change, including the available task, output, human decision and build-result records. The bundle must distinguish directly observed facts from imported assertions.
Boundary
A proof bundle is not automatically a complete vault backup or a demonstrated restore process. Portability does not establish completeness, legal admissibility or regulatory compliance, and cryptographic integrity does not make an imported assertion true.
Concept illustration
Concept illustration 07 — Narrow, evidence-supported claims
State only what the available evidence supports, with its scope and limits.
Purpose
SBBX treats a capability claim as something that must be supported by identifiable evidence. A design proposal, a committed implementation, a successful test and a released product are different states.
How it is intended to work
A meaningful claim identifies the subject, version, evaluated environment, method and limitations. Evidence about one runtime or device must not silently become a claim about every deployment.
Example
A successful local test can support the behaviour exercised in that local environment. It does not automatically establish production readiness, complete coverage or behaviour on a physical phone.
Boundary
An attractive diagram, merged pull request or green indicator is not sufficient evidence for every capability. Unknowns and open gaps remain explicit until the relevant evidence supports a narrower or stronger conclusion.
Concept illustration
What SBBX can establish / What SBBX cannot establish
The left column applies only when corresponding evidence exists.
Can establish
Only when corresponding evidence exists.
- Whether evaluated bytes match expected bytes.
- Whether an integrity chain verifies.
- Whether a supported signature verifies for the stated key role.
- The verifier result for the supplied bundle.
Cannot establish
These remain outside what cryptography can support.
- That captured source statements are factually true.
- That an AI interpretation is correct.
- That hallucinations are impossible.
- Why a byte changed.
- Actor intention.
- Events that occurred outside the captured evidence boundary.
Architecture layers
Capture boundary
Declared scope, consent binding and canonical serialisation.
- Consent binding
- Declared work boundary
- Canonical serialisation
Integrity layer
Append-only hash linking of canonical records.
- SHA-256 record digests
- Append-only linking
- Tamper-evidence
Role separation
Capture, approval and consent are distinct, attributed roles.
- Capture role
- Approval role
- Consent role
Local-first runtime
Operation without dependency on a remote service.
- Local execution
- No mandatory network path
- Operator-held data
Portable proof bundle
A self-contained export intended for independent checking.
- Records + links
- Declared key roles
- Verifier inputs
Offline verifier
Deterministic evaluation of the supplied bundle only.
- Byte comparison
- Chain evaluation
- Signature evaluation
Capability states
A capability may be claimed only when its claim state is active.
| Capability | State | Claim | Note |
|---|---|---|---|
| Canonical record model | CANDIDATE | NOT ACTIVE | Specification under review inside the M1 scope. |
| Append-only integrity chain | CANDIDATE | NOT ACTIVE | Design and reference logic in progress; not ratified. |
| Offline independent verifier | PLANNED | NOT ACTIVE | Planned for the M1 acceptance set. |
| Portable proof bundle format | PLANNED | NOT ACTIVE | Format drafted; no released artifact is claimed. |
| Android durable encrypted-at-rest vault | DEFINED | NOT ACTIVE | Defined intent only. Claim is not active. |
| SYGNET policy control plane | DEFINED | NOT ACTIVE | Post-M1 architecture preview. Not in the current product. |